


The magazine of innovation in Africa
Digital Sovereignty in Africa: A Conversation with Léon Brandre
Published on July 31, 2026
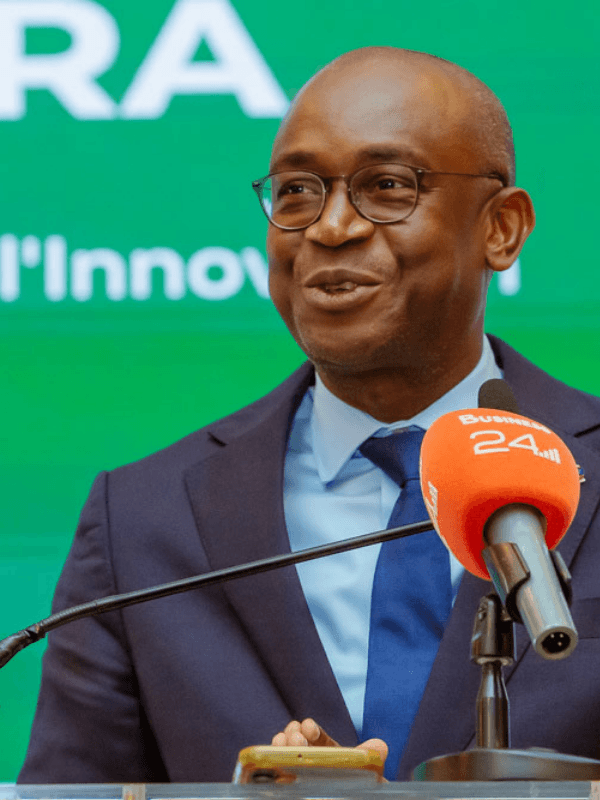
Where does Africa stand on digital sovereignty? We put that question to Léon Brandre, head of Groupe DPSE, an Abidjan-based firm specializing in personal data protection, licensed by Côte d'Ivoire's telecommunications regulator, the ARTCI. Brandre also played a role in revising ECOWAS's Additional Act on data protection.
Even today, a large share of African companies' data still sits abroad, in the United States, Europe or Asia. During the first wave of digitization, that choice made sense: the cloud giants offered remarkable tools, ready to use, at a time when digital sovereignty wasn't yet part of the conversation.
That model is now running out of road. With data protection legislation now adopted by 80% of African Union member states (44 countries) and ECOWAS updating its guidelines under the push of the Malabo Convention, regulation is imposing a new paradigm: sovereignty and data localization are no longer optional.
More than a decade after Côte d'Ivoire's 2013 data protection law and the ARTCI's declarative regime came into force, what's your assessment?
"That's a tall order, asking me to stand in the regulator's shoes. But let me try, starting from where it all began: the entry into force of Law No. 2013-450 of 19 June 2013 on the protection of personal data. That law deserves credit for laying the historical foundations of a legal framework. The work done by the ARTCI and by every player in the digital ecosystem has raised awareness, particularly in heavily regulated sectors like banking and telecoms.
That said, we're still too caught up in a box-ticking mindset. For many organizations, compliance still means filing paperwork with the regulator once, rather than treating it as an ongoing discipline. What's still sorely missing is a genuine privacy culture built into business processes, what's known as Privacy by Design. Too many executives still see data protection as a cost center or a legal constraint, rather than as a lever for digital trust and commercial performance. The real task now is to move from paper compliance to a culture of operational practice. I'm placing a lot of hope in the imminent entry into force of the revised Additional Act on data protection, which we helped revise between 2024 and 2025 with support from German cooperation (GIZ), on behalf of the ECOWAS Commission and its member states. Once transposed, it will build a new compliance culture and give this ecosystem resilient, operational tools."
Given the patchwork of legal frameworks, what do you tell an Ivorian business leader: hunker down behind national law, or get ahead of a harmonized regional standard?
"The advice we give our clients is a pragmatic one: national markets are simply too narrow, so companies are all but forced toward sub-regional ambition. A leader who builds a strategy around Ivorian law alone is putting up walls that will block future expansion.
So we advise aiming for the highest common denominator. By adopting standards aligned with regional and international best practice today, whether that's the revised ECOWAS Additional Act or GDPR principles, an Ivorian company buys itself strategic agility. It becomes interoperable by default. Data protection shouldn't be a border, it should be a passport into the single African market, which digital governance will underpin."
That single-market vision is exactly what Hodi works to serve: a pan-African cloud present across some thirty countries and territories, with services aligned to both national laws and emerging regional frameworks, hosted in local Tier III data centers.
Between the Malabo Convention and ECOWAS's initiatives, where is Africa headed by 2030?
"We're moving, unavoidably, toward deep convergence and harmonization. The gradual ratification of the Malabo Convention, together with the momentum behind ECOWAS's work, which our firm is proud to contribute to technically, points to a clear trajectory: the emergence of a unified digital trust space.
Within three to five years, we'll see mutual recognition mechanisms take shape between Africa's data protection authorities, something like an African data protection board, built on the revised Additional Act and on cooperation already underway between these authorities. Penalties will become more consistent and more dissuasive. Companies that get ahead of this regional integration will turn it into an advantage, while latecomers will bear the full cost of a compliance effort that comes too late and too fragmented."
Is a fully sovereign African cloud a realistic ambition?
"For a firm like ours, dealing daily with the realities of data governance, full sovereignty is a technical illusion in the short term. People consistently overlook the lower layers of the value chain. Having a data center on Ivorian soil is excellent, but who makes the processors? Who maintains the operating systems? Who manages the undersea cables or the international routing infrastructure?
Sovereignty isn't declared by having an IP address in Abidjan. It's built through infrastructure redundancy, control over source code, and rigorous contracting around technological dependencies."
Hodi is a French company, and therefore subject to GDPR, while hosting its clients' data in their own countries. For an Ivorian company whose data never leaves the country, what difference does that actually make?
"That's an excellent question, because it goes to the heart of what's at stake for digital sovereignty in West Africa today. To answer directly: yes, it changes a great deal, and on the whole it's very good news for the Ivorian company, though it does raise one specific legal point worth watching. There are really three major effects to understand.
First, an immediate boost to Ivorian security and compliance. Even though the data stays in Abidjan or Yamoussoukro, Côte d'Ivoire's 2013 law requires the data controller to guarantee the security and confidentiality of the data it collects. By choosing an operator bound by GDPR, the Ivorian company benefits, as a side effect, from some of the strictest cybersecurity standards in the world: encryption, regular audits, data isolation, mandatory breach notification. It's a real source of peace of mind, and it helps the company meet ARTCI's requirements without reinventing the wheel.
Second, there's no bureaucratic obstacle course around data transfers. Because the physical servers are located in Côte d'Ivoire, there's no cross-border transfer involved. The Ivorian company avoids the heavy prior-authorization process with the ARTCI. In other words, it gets the best of both worlds: the rigor of a European-style data processing agreement, applied to data that stays 100% local.
Finally, the point worth watching, and it's the only real caveat: extraterritoriality risk. Because the operator is a European entity, it remains subject to European jurisdictions. If a European judge ordered it to hand over data, it would find itself caught between European law and Ivorian sovereignty. The precaution to take, when signing the contract, is to write in a clear clause: in the event of a dispute, the operator notifies the country of origin of the data."
Hodi fully owns that last point. And it deserves some perspective: this isn't a weakness specific to our model, it's the condition faced by any hosting provider tied to any jurisdiction whatsoever. In late 2025, a North American court ordered OVH to hand over data that was, in fact, stored in Europe, on the grounds that it operated commercially within that court's jurisdiction. OVH pushed back, leaning precisely on its own national law, which prohibits that kind of transfer outside official channels of judicial cooperation. The case is still pending, but it makes the point clearly: extraterritoriality is a risk for everyone, including operators widely seen as the most sovereign, and it's often the host's legal grounding that becomes the shield rather than the gap.
Two things need to be kept separate here: where the data resides, which stays African, and the operator's legal accountability, which is European. Nothing moves back to Europe, except the bar for what's required. And the clause Léon Brandre suggests, notifying the country of origin in the event of a legal request, is meant to be spelled out in black and white in our data processing agreement.
To close, what's Africa's priority challenge: building data centers, or building skills?
"Investing in data centers without training the people who run and govern them is like building empty vaults. Africa's real challenge isn't physical, it's intangible: skills, expertise, and a culture of data.
Infrastructure is a commodity you can buy or rent. Governance intelligence, data architecture, the ability to audit security and design trust policies, none of that can be improvised. Groupe DPSE is pushing hard for a focus on top-tier human capital. Africa will only be sovereign over its data once it has a critical mass of engineers, data protection officers, specialized lawyers, and informed executives, people capable of setting their own terms. That's our fight, and it's the very reason Groupe DPSE exists."
It's a view Hodi's pan-African team shares completely. In that spirit, Hodi supports the continent's incubators and early-stage startups through the Hodipulse program, and is actively working to build a network of African cloud experts, with a system of badges and certifications, in each country where the company operates.
More on that soon.